


|
This is the web edition of the original ⮫ AC500-S safety user manual, version 1.3.2. This web edition is provided for quick reference only. The original safety user manual must be used to meet functional safety application requirements. |
Instead of manually checking the safety programming guidelines, you can use ABB software tool "AC500-S Safety Code Analysis" (SCA) to automatically check most of the safety rules.
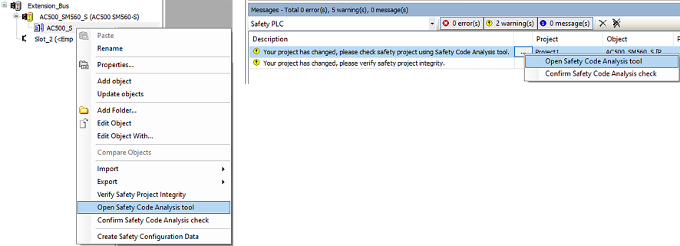
When a new safety project is created in Automation Builder or when a safety project is modified, a warning message appears prompting the user to check the safety project with the SCA tool.
-
Open the SCA tool. Either from the context menu of the safety application node or from the messages window.
-
With Automation Builder version < 2.6.0, SCA tool must be installed as a stand-alone tool.
It can be downloaded for free from ⮫ www.abb.com/plc.
The installation of the stand-alone SCA tool is described ⮫ here.
-
Follow the described workflow in the integrated help of SCA tool to check your safety project.
-
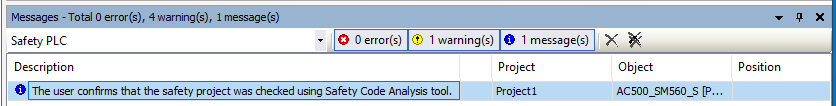
In Automation Builder, confirm the successful check with the SCA tool.

-
Do the manual checks. There are rules which still have to be checked manually⮫ Table 1055 “Safety programming rules to be checked manually”. AC500-S SCA tool is not able to detect them in the safety application program.
|
Rule for manual check in AC500-S Programming Tool |
Comments (relevance for AC500-S) |
|---|---|
|
Verify that the watchdog is activated. Verify that the watchdog time is set sufficiently shorter than the process failure response time. |
Use a special library POU SF_WDOG_TIME_SET⮫ “SF_WDOG_TIME_SET” |
|
Verify that there is only one task. |
AC500-S supports only one task, thus, there is no need for this check. |
|
Verify that, other than standard libraries, only libraries certified for safety applications are used. |
These rules are included in ⮫ “Checklist for creation of safety application program” |
|
For each POU, verify that there are no unnecessary state variables. |
|
|
Verify that the following holds for all function blocks: If more than one variable is used to store state information, encapsulate these variables into their own function block and only use calls on this function block to change the state. |
|
|
Verify that the compiler reports neither errors nor warnings when compiling the application. |
|
|
For each POU, verify that variables are not re-used later on with a different meaning. |
|
|
Verify that the names of safety POUs start with "S_". Verify that the names of non-safety POUs do not start with "S_". |
These rules have to be checked only if you plan to implement not only safety but also non-safety functions on AC500-S safety CPU. In typical applications with AC500-S it is not the case, because non-safety functions are realized on non-safety CPUs. |
|
Verify that names of safety variables start with "S_". Verify that names of global safety variables start with "GS_". Verify that names of safety inputs start with "IS_". Verify that names of safety outputs start with "OS_". Verify that names of non-safety variables do not start with either "S_", "GS_", "IS_" or "OS_". |
|
|
Verify that names of global variable lists containing non-safety variables do not start with S_. |
|
|
Verify that names of global variable lists containing safety variables start with S_. |
|
|
For each non-safety POU, verify that it does not write to any safety variable. |